Software Trust Manager
Signed. Secured. Deployed.
Know what’s behind every release.
Modern software teams release across more repositories, pipelines, artifacts, and environments than ever before. DigiCert Software Trust Manager helps organizations govern signing, automate secure workflows, and bring release risk into view—so you can ship trusted software at speed.
Software delivery has scaled. Release trust hasn’t always kept up.
Signing, security findings, policies, and approvals often live across different systems, teams, and pipelines. That can make it harder to consistently answer the questions that matter.

Who is allowed to sign?
Signing credentials, access, approvals, and policies can vary across teams and development environments.

What's behind the release?
Dependencies, known vulnerabilities, SBOM information, and security-scan results may need to be correlated across disconnected tools.

What happens when risk changes?
A release that passes its original security checks can still be affected by vulnerabilities identified after deployment.
A signature is only part of the trust decision
Code signing establishes the authenticity and integrity of software. But teams also need visibility into what a release contains and the known risk associated with it.
Secure Releases connects supported software releases with dependency, vulnerability, CVSS, SBOM, and security-scan information—helping teams understand which releases may require attention—all within Software Trust Manager.
You can define vulnerability and SBOM-based requirements and apply those conditions within signing and release workflows.
You determine the requirements, thresholds, and policies that govern release decisions.

See it in action
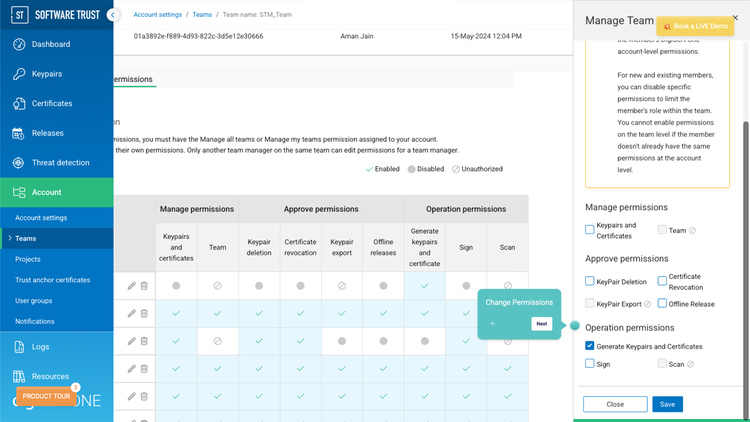
See how DigiCert Software Trust Manager integrates signing into modern development workflows while keeping signing credentials protected and governance centralized.
Explore software release trust resources
Strategic Guide
Signed. Secured. Deployed.
Why modern software organizations need to govern not only how software is signed, but how release trust is established and maintained.
Readiness Checklist
Are Your Software Releases Ready to Deploy?
Assess your release process across signing governance and control, release visibility, vulnerability monitoring, policy, and evidence.
Upcoming Webinar
What’s Behind the Release?
5 questions software leaders should ask before and after every deployment.
Ready to secure every release?
Protect signing credentials, automate approved workflows, bring release risk into view, and maintain clear evidence of what your teams release with DigiCert Software Trust Manager.
{{anchor:talk}}