Internal and air-gapped environments
Automate certificate lifecycles in isolated networks while preserving the network controls your security architecture requires.
DigiCert Trust Lifecycle Manager (TLM) supports two isolation models: a private, on-premises DigiCert ONE deployment for environments that must keep private certificate lifecycle operations inside the network boundary, and cloud-hosted TLM accessed through an approved proxy or DigiCert sensor when controlled outbound connectivity is permitted.
The appropriate architectural model depends on your actual isolation level, certificate trust requirements, and the deployment options supported for your account. If you require a fully managed on-premises deployment, contact DigiCert to speak with the extended DigiCert team and determine the best architecture for your environment.
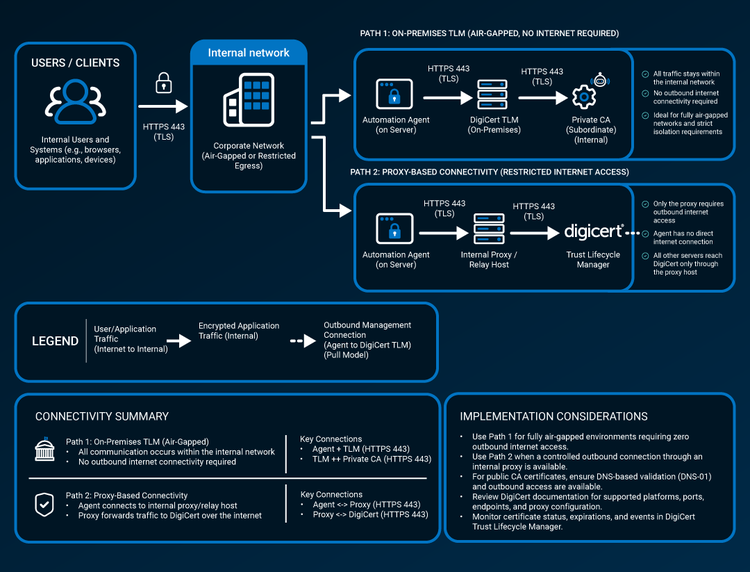
Fully disconnected environments keep private-trust lifecycle operations inside the boundary. Restricted environments can centralize cloud management through a controlled proxy path. Please speak to a DigiCert solutions architect to determine the optimal architecture for your specific needs.
Why this scenario matters
A truly disconnected network has no routable path to external services, whereas a restricted network allows controlled outbound connectivity through a proxy, DMZ, or sensor, and that distinction determines which certificate-management architecture is most viable.
Private-trust certificates are typically the best fit when issuance, renewal, and deployment must stay entirely within the network boundary. Public-trust certificates can still be used on isolated services, but issuance depends on an external CA and domain-validation process. In a true air gap, issuance or renewal must happen outside the boundary, and the certificate must be transferred through an approved process rather than managed end-to-end from inside the isolated network.
How DigiCert fits
- Fully disconnected private-trust management — a private on-premises DigiCert ONE deployment can provide Trust Lifecycle Manager and private-trust certificate services within an organization-controlled environment.
- Controlled egress through a proxy — DigiCert agents can connect through a customer proxy or a DigiCert sensor acting as a proxy, so managed hosts do not need direct internet access.
- Local execution close to the target — agents manage certificates on supported Windows and Linux hosts. DigiCert Sensors provide network-level discovery, automation, integrations, and proxy services.
- CA integration and governance — TLM can use DigiCert Private CA and connectors to supported external CAs, allowing certificate policy and lifecycle management to be centralized around the chosen trust model.
At a glance
- Environment: a fully disconnected network, or a restricted network where direct internet access from managed systems is prohibited.
- DigiCert deployment model: fully disconnected private on-premises DigiCert ONE/TLM for private-trust lifecycle operations; or restricted-egress cloud-hosted TLM reached through an approved customer proxy or DigiCert sensor.
- Certificate trust model: private trust is the natural fit for zero-egress issuance and renewal. Public-trust issuance depends on an external public CA and domain-validation path. A true air gap therefore requires an approved transfer process.
- What to verify before deployment: availability of the private on-premises deployment model, supported agents/sensors, CA architecture, internal DNS and trust stores, proxy destinations and ports, and the organization's update/patch transfer process.
Technical implementation details
Exact network destinations, local trust-store requirements, supported operating systems, proxy configuration, CA connector prerequisites, and enrollment behavior vary by deployment. Confirm the current DigiCert documentation before designing firewall rules or implementation procedures, especially for private on-premises DigiCert ONE environments. Contact DigiCert to determine the best architecture for your environment.
- DigiCert agents and sensors — understand which component performs host-level automation, network-level automation, integrations, and proxy services.
- Agent system and network requirements — review current agent platform, local-host, DigiCert ONE, DNS, and connectivity requirements, including notes for on-premises DigiCert ONE.
- Sensor system and network requirements — review sensor placement and network requirements for cloud-hosted or local DigiCert ONE connectivity.
- DigiCert On-prem CA connector — see how Trust Lifecycle Manager connects to a customer-hosted DigiCert Private CA and what sensor and CA prerequisites apply.
Frequently asked questions
Ready to evaluate your environment?
See how DigiCert Trust Lifecycle Manager can support certificate lifecycle automation across your enterprise.