Web server behind a firewall
Automate certificate lifecycles while keeping web servers protected behind your corporate perimeter.
DigiCert Trust Lifecycle Manager (TLM) can support certificate lifecycle automation for web servers that sit behind a corporate firewall. With an agent-based deployment model and a validation approach appropriate to the environment, organizations can centralize visibility, policy, automation, and lifecycle monitoring across certificate operations.
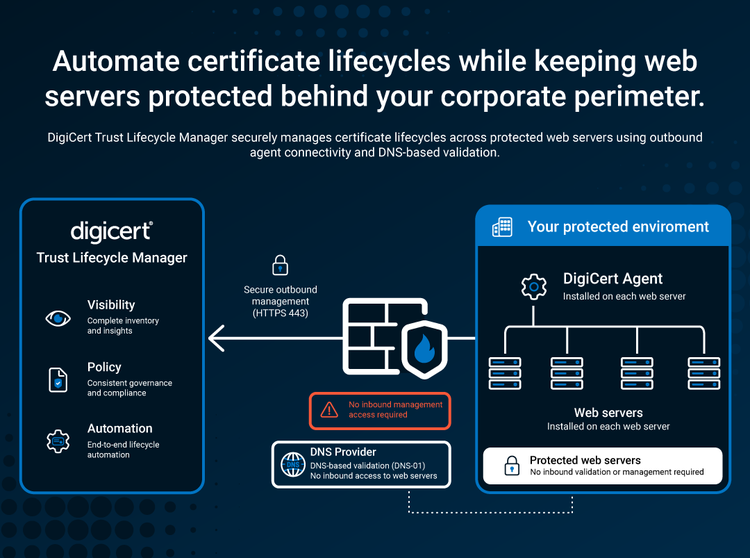
High-level deployment concept: Trust Lifecycle Manager centrally governs certificate automation for protected web servers, with the local agent operating inside the enterprise environment.
Why this scenario matters
Web servers behind firewalls are common in enterprise environments, but certificate renewal still has to happen reliably. As public TLS certificate lifetimes shorten, manual renewal and deployment processes become harder to sustain at scale.
The key question is not whether the firewall prevents automation. It is whether the certificate-management architecture fits the organization's network, validation, security, and operational requirements.
How DigiCert fits
Centralized lifecycle management
Use TLM to maintain certificate inventory, create automation profiles, manage lifecycle events, and monitor certificate status from a centralized console.
Agent-based web-server automation
A DigiCert agent runs in the protected environment and supports managed certificate operations on supported web servers.
Validation flexibility
DNS-based validation can avoid inbound validation traffic to the protected web server. HTTP-based validation remains available where the environment supports it.
Operational visibility
Centralized monitoring helps teams see certificate and automation status across the managed environment.
At a glance
- Environment: one or more supported web servers protected by a corporate firewall.
- DigiCert deployment model: Trust Lifecycle Manager with a DigiCert agent on the managed web-server host.
- Typical validation approach: DNS-based validation is often a strong fit for restrictive inbound network policies; other supported validation methods may also be used.
- What to verify before deployment: supported systems, network requirements, DNS/DCV requirements, certificate profiles, and automation workflow.
Technical implementation details
Exact ports, endpoints, DNS integration requirements, supported platforms, validation behavior, proxy options, and deployment procedures can vary by environment and should be confirmed in the current DigiCert documentation.
- DigiCert agents and sensors — understand the role of agents and sensors and how agents manage certificates on web servers.
- Agent system and network requirements — review current operating-system, outbound connectivity, proxy, DNS, and local-host requirements.
- Managed automation solution — review DigiCert managed automation capabilities for servers, appliances, cloud services, and vaults.
- DNS integrations for domain validation — see how DNS integrations are assigned to agents and other managed systems for automated domain validation.
Frequently asked questions
Ready to evaluate your environment?
See how DigiCert Trust Lifecycle Manager can support certificate lifecycle automation across your enterprise.