CTO Q&A: Rethinking resilience across AI ecosystems
Co-authored by Mike Nelson
Where can the risk travel? Rethinking resilience for AI ecosystems
B. Braun Chief Product Security Officer Joern Lubadel and DigiCert Field CTO Mike Nelson explore how AI is changing the way security teams think about dependencies, trust, and resilience.
The Cyber Resilience Act is often discussed through the lens of compliance: software bills of materials, vulnerability management, documentation, and reporting requirements.
But beneath those requirements is a broader idea that becomes especially important as AI takes on a larger role in enterprise systems: modern technology no longer operates in isolation.
Applications depend on cloud services. AI agents call models and tools. Systems retrieve information from external sources. Devices, workloads, APIs, and data cross technical and organizational boundaries. A weakness in one place can create consequences somewhere entirely different.
That is a challenge Joern Lubadel, Chief Product Security Officer at B. Braun, has been thinking about as he considers the broader implications of the Cyber Resilience Act. His question goes well beyond compliance: What if the most important risk is not where a vulnerability starts, but where it can travel?
We brought Lubadel together with DigiCert Field CTO Mike Nelson to discuss what that idea means for cybersecurity, AI trust, and resilience.
DigiCert: Joern, what about the CRA is making you think differently?
Joern Lubadel, B. Braun: Most conversations about the Cyber Resilience Act focus on SBOMs, vulnerability management, documentation, and compliance. All of those things matter.
But what keeps drawing my attention is the emphasis on dependencies and connected environments
A few years ago, we could often think about a digital product largely as an individual system. That is becoming much harder. What looks like one product may depend on cloud services, external knowledge sources, AI models, agents, healthcare platforms, connected medical technologies, and other systems outside its immediate boundary.
So the question is no longer simply, “Is this product secure?”
We also have to ask what it depends on, what depends on it, and how far the consequences of a weakness could travel through that environment.
To me, that is one of the more interesting ideas behind the CRA. It pushes us toward thinking about ecosystems, not just components.
Mike Nelson, DigiCert: I agree, and AI makes that shift much more visible.
Agents are useful precisely because they connect to other things. They consume information, call tools, interact with applications, and take action.
That means understanding the security of an individual component no longer tells you everything you need to know about the larger environment.
Risk increasingly lives in the relationships between components, not just inside the components themselves.
Mike: Does that mean we need to rethink how we prioritize vulnerabilities?
Joern: I think we need to add another dimension to how we look at them.
We spend a lot of time identifying vulnerabilities, and rightly so. But the existence of a vulnerability does not tell you the full story. Some weaknesses remain isolated. Others may technically be exploitable but never reach anything consequential. What matters is whether a weakness can participate in a credible path to something important.
That changes the question from “Where is the vulnerability?” to “Where could this vulnerability lead?”
If we understand those paths, we can make better decisions about where to intervene. We may not be able to eliminate every weakness, but we can identify the paths that matter most and determine where they can be interrupted, contained, or detected.
That, to me, is a much more practical definition of resilience.
Mike: Context becomes critical
Imagine two identical vulnerabilities. One exists in a system with almost no access to anything else. The other exists in a workload that an AI agent can reach, and that agent has permission to access sensitive data or take action in another application.
The vulnerability may be the same. The consequence is not.
That is why reachability matters so much. What can this system communicate with? What does it trust? What authority does it have? And what happens if that trust is misplaced?
AI does not change the fundamentals of cybersecurity, but it makes those relationships much harder to ignore.
DigiCert: Where do trust boundaries fit into that picture?
Joern: Once you start tracing those paths, trust boundaries appear everywhere.
Information comes in from an external source. A service accepts data it did not create. An AI agent consumes context from another component. A downstream system acts on information that originated somewhere else.
At every one of those boundaries, a trust decision is being made, whether we have explicitly designed for it or not.
The question is not only, “Do we trust this?” It is, “Can we explain why we trust it, and can we verify that trust?”
That distinction becomes increasingly important as environments become more connected.
Mike: Historically, many trust decisions have been implicit.
A system trusts something because it came from a known network, application, account, or environment. That becomes harder to sustain when agents and workloads move across clouds, applications, and organizational boundaries.
Trust has to become more explicit.
We need to be able to answer questions such as:
- What is this workload or agent?
- Can I verify its identity?
- Who is responsible for it?
- What is it authorized to do?
- Has the information it provided been altered?
- Is its authority still valid?
Those are not just access questions. They are verification questions.
Mike: This seems to make technologies such as PKI more relevant, not less.
Joern: That was one of the things I kept coming back to.
The further I followed this idea, the more I found myself looking at technologies we have used for years: public key infrastructure, workload identities, device identities, digital signatures, attestation, and lifecycle management.
Their relevance is not that they are new. It is that they solve a problem that becomes more difficult every time we add another dependency.
As ecosystems become more dynamic, trust becomes less about ownership and more about verification.
A system needs evidence of who or what it is interacting with, whether information has maintained its integrity, and whether an identity or credential is still valid.
Lifecycle management is especially important here. Trust is not something you establish once. Certificates expire. Keys rotate. Identities are revoked. Systems change. Relationships evolve.
Without continuous maintenance, verified trust can gradually become assumed trust.
Mike: That is exactly where cryptographic trust becomes valuable.
PKI, digital signatures, and verifiable identities give systems evidence they can validate independently.
An agent may need to prove its identity to a tool. A service may need to confirm that a request really came from an authorized agent. A downstream system may need evidence that information has not been modified.
Cryptography gives you a foundation for making those decisions.
But we also need to be precise about what it proves.
A digital signature can tell you who signed something and whether it changed afterward. It cannot tell you whether an AI-generated result is factually, clinically, or contextually correct.
Identity and integrity are important parts of trust, but they do not replace validation, policy, or human judgment.
Mike: AI environments change constantly. How should security teams think about that?
Joern: I think this is where static evidence starts to become insufficient on its own.
We often treat SBOMs, threat models, and risk assessments as deliverables. But their greater value may be as signals about a changing environment.
A model changes. An agent receives a new permission. Someone adds an integration. A workload begins consuming data from a new source.
None of those events necessarily creates a new vulnerability.
But each can create a new relationship, and that relationship may create a path that did not exist before.
So the question shifts from “Which vulnerabilities exist?” to “What changed, and did that change create a credible new path?”
That requires continuous awareness rather than periodic snapshots.
Mike: And that is where automation and human judgment have to work together.
Automation can help keep inventories current, correlate dependencies, and identify changes in reachability, identity, or trust.
But deciding whether a consequence actually matters still requires context and accountability.
A system may be able to tell you that something changed. A person still needs to decide whether that change is acceptable, whether it creates meaningful risk, and what action should follow.
That combination gives security teams a much more dynamic view of risk.
DigiCert: Does that change how you both think about the Cyber Resilience Act itself?
Joern: For me, it does.
The compliance requirements are necessary, but I think the more interesting contribution of the CRA is the way it encourages us to think about dependencies, connectedness, and consequences.
That becomes particularly important in AI-enabled ecosystems.
The question I keep returning to is simple:
How far can the consequences of a weakness travel through a connected ecosystem?
When you ask that, you stop looking only at individual components and start looking at the relationships connecting them.
That feels less like a compliance exercise and more like a resilience challenge.
Mike: And I think AI makes that resilience challenge even more urgent.
Agents, models, workloads, applications, and data sources form increasingly dynamic ecosystems. Securing those environments requires more than finding weaknesses. We also need to understand relationships, verify trust across boundaries, and know how far authority can extend.
That is why AI trust cannot be reduced to securing the model itself.
As AI becomes more autonomous, we need to know what is acting, what it is allowed to do, what it depends on, and whether those relationships can be verified.
Joern’s question is a useful one because it reframes the entire discussion.
The most important security question may no longer be simply:
“Where is the vulnerability?”
It may be:
“Where can it take us?”
Customer headshot:
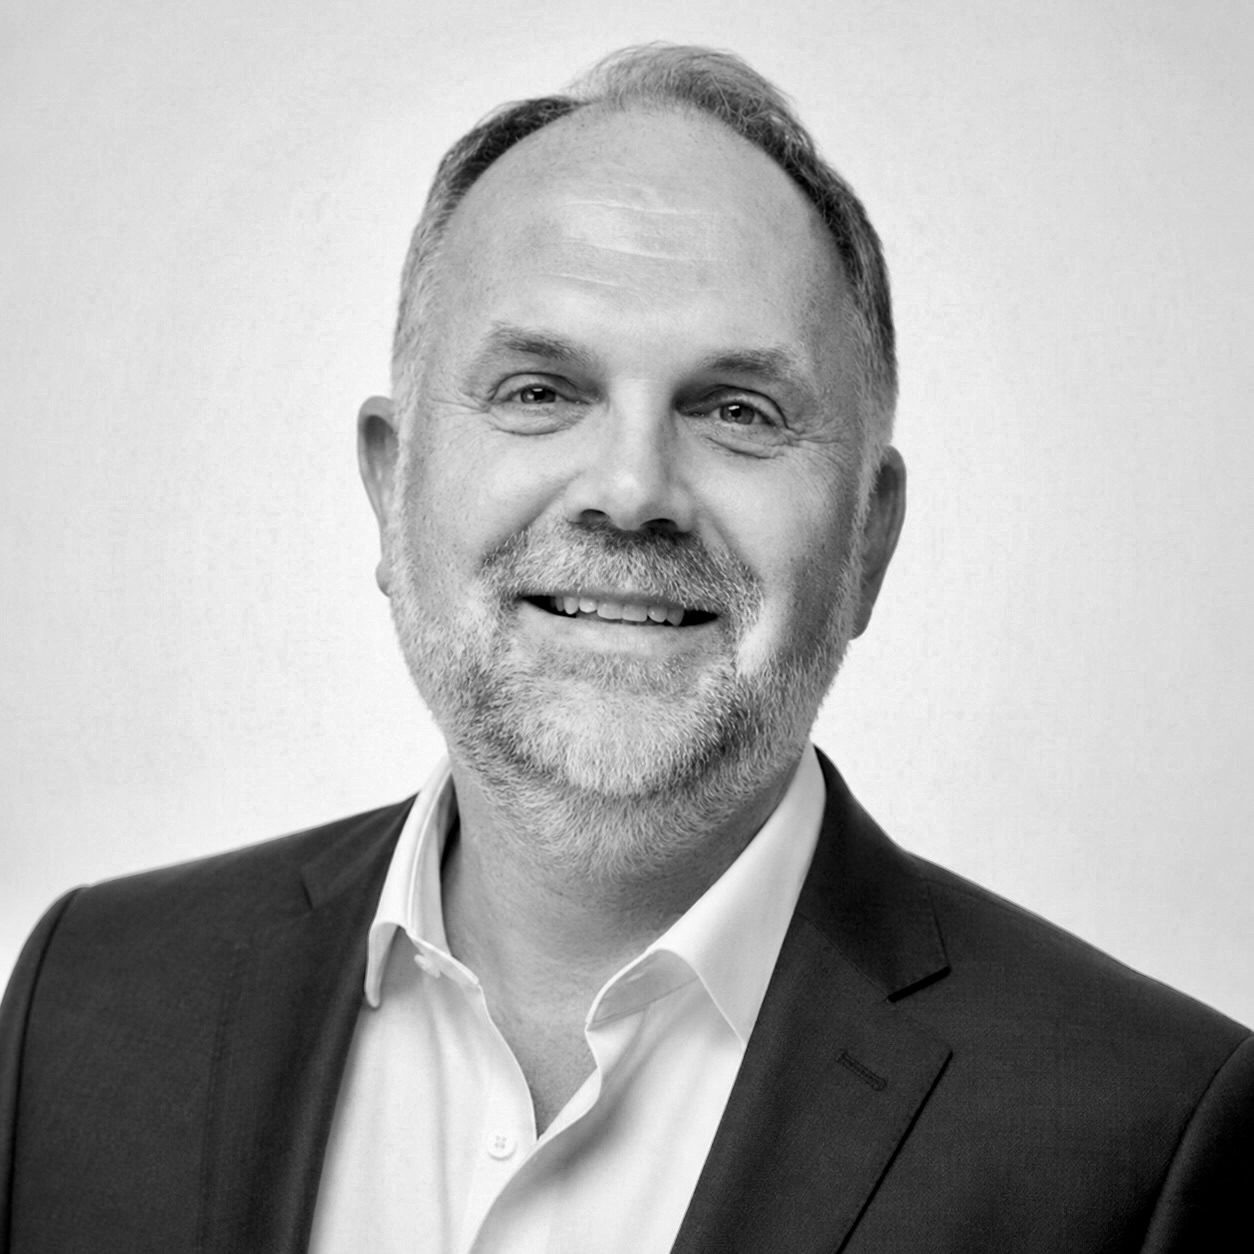
Joern Lubadel headshot
Bio:
Joern Lubadel is Global Head of Product Security at B. Braun, with more than 25 years of experience spanning healthcare technology, cybersecurity, software, and regulatory affairs. He is a recognized voice in medical device cybersecurity and actively contributes to international industry, regulatory, and standards initiatives through leadership roles in MedTech Europe and APACMed, participation in global standards development activities, and contributions to regulatory working groups.
Joern is passionate about digital trust and believes organizations must continuously challenge assumptions and adapt to an evolving threat landscape. While security by design remains essential, he advocates for cyber resilience and agility as the foundations of healthcare systems that can maintain safety, trust, and operational continuity in the face of constant change.
Working at the intersection of innovation, cybersecurity, and regulation, Joern helps organizations navigate complex challenges while keeping patient and customer trust at the center of decision-making.
Subscribe to the blog
-
DigiCert is a global leader in intelligent trust, securing people, data, and devices with AI-powered solutions built to stop threats today and prepare for a quantum-safe future.
-
-
© 2026 DigiCert, Inc. All rights reserved.
Legal Repository Audits & Certifications Terms of Use Privacy Center Accessibility Cookie Settings